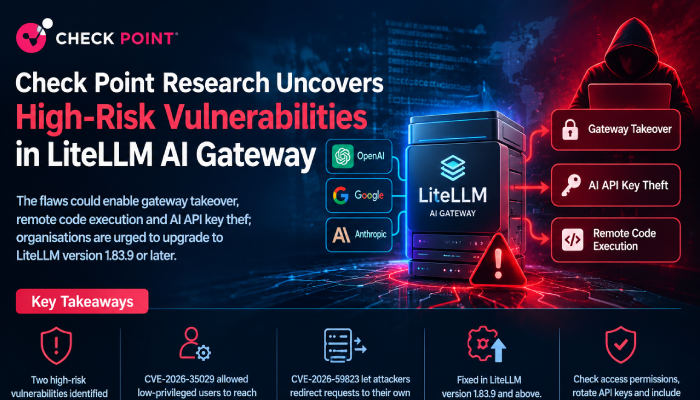
The flaws could enable gateway takeover, remote code execution and AI API key theft; organisations are urged to upgrade to LiteLLM version 1.83.9 or later.
Check Point Research has identified two high-risk vulnerabilities in LiteLLM, an open-source large language model (LLM) gateway used to connect applications with AI providers such as OpenAI, Google and Anthropic. The vulnerabilities could expose enterprise AI infrastructure to administrative takeover, credential theft and unauthorised use of AI services.
According to Check Point Research, LiteLLM records approximately 97 million downloads per month and more than 59,000 GitHub stars, highlighting the potential reach of security weaknesses in widely deployed AI infrastructure.
The vulnerabilities, tracked as CVE-2026-35029 and CVE-2026-59823, affect different aspects of gateway security. CVE-2026-35029 involves an access-control flaw that allowed users with limited privileges, including read-only access, to reach administrative functions. Researchers demonstrated that the weakness could enable access to server files, administrator credential changes and the execution of externally sourced code.
CVE-2026-59823 is a server-side request forgery (SSRF) vulnerability that allowed users to redirect gateway requests to attacker-controlled servers. Because these requests could carry credentials used to authenticate with AI providers, exploitation could expose API keys without requiring a direct compromise of the providers themselves. Stolen keys could subsequently enable unauthorised AI usage and unexpected costs.
“AI gateways are becoming critical infrastructure, holding privileged access to models, credentials and sensitive data. Weak access controls or insecure request routing can turn a single vulnerability into a broader enterprise security incident.”
The risks are significant because LLM gateways sit between enterprise applications and AI services. They manage provider credentials, user permissions, model routing and usage tracking, making them attractive targets for attackers seeking access to AI resources.
Check Point Research said it responsibly disclosed both vulnerabilities to LiteLLM through a coordinated disclosure process that began in October 2025. The issues have been fixed in LiteLLM version 1.83.9 and later releases.
Organisations should prioritise upgrading all LiteLLM deployments, including instances embedded in internal tools and other platforms. Security teams should review gateway access permissions, remove unnecessary accounts and rotate AI provider API keys where unauthorised access may have occurred before patching.
The findings also underline the need to include AI gateways in vulnerability assessments and penetration testing. As organisations integrate LLMs into business-critical applications, securing the infrastructure connecting those systems to AI providers is becoming an essential part of enterprise cybersecurity.